Buy 61.eu ?
We are moving the project
61.eu .
Are you interested in purchasing the domain
61.eu ?
domain@kv-gmbh.de · 0541-91531010
Buy 61.eu ?
What is an alternative to iptables?
An alternative to iptables is nftables, which is a newer and more powerful packet filtering framework for Linux. Nftables provides a more user-friendly syntax and better performance compared to iptables. It also offers additional features such as stateful firewalling, easier rule management, and better integration with the Linux kernel. Overall, nftables is a modern replacement for iptables and is recommended for those looking for a more advanced and efficient packet filtering solution. **
Hello, I have a question regarding iptables.
Sure, I'd be happy to help. What specific question do you have about iptables? **

Similar search terms for Iptables
Top-Angebote
Products related to Iptables:
-
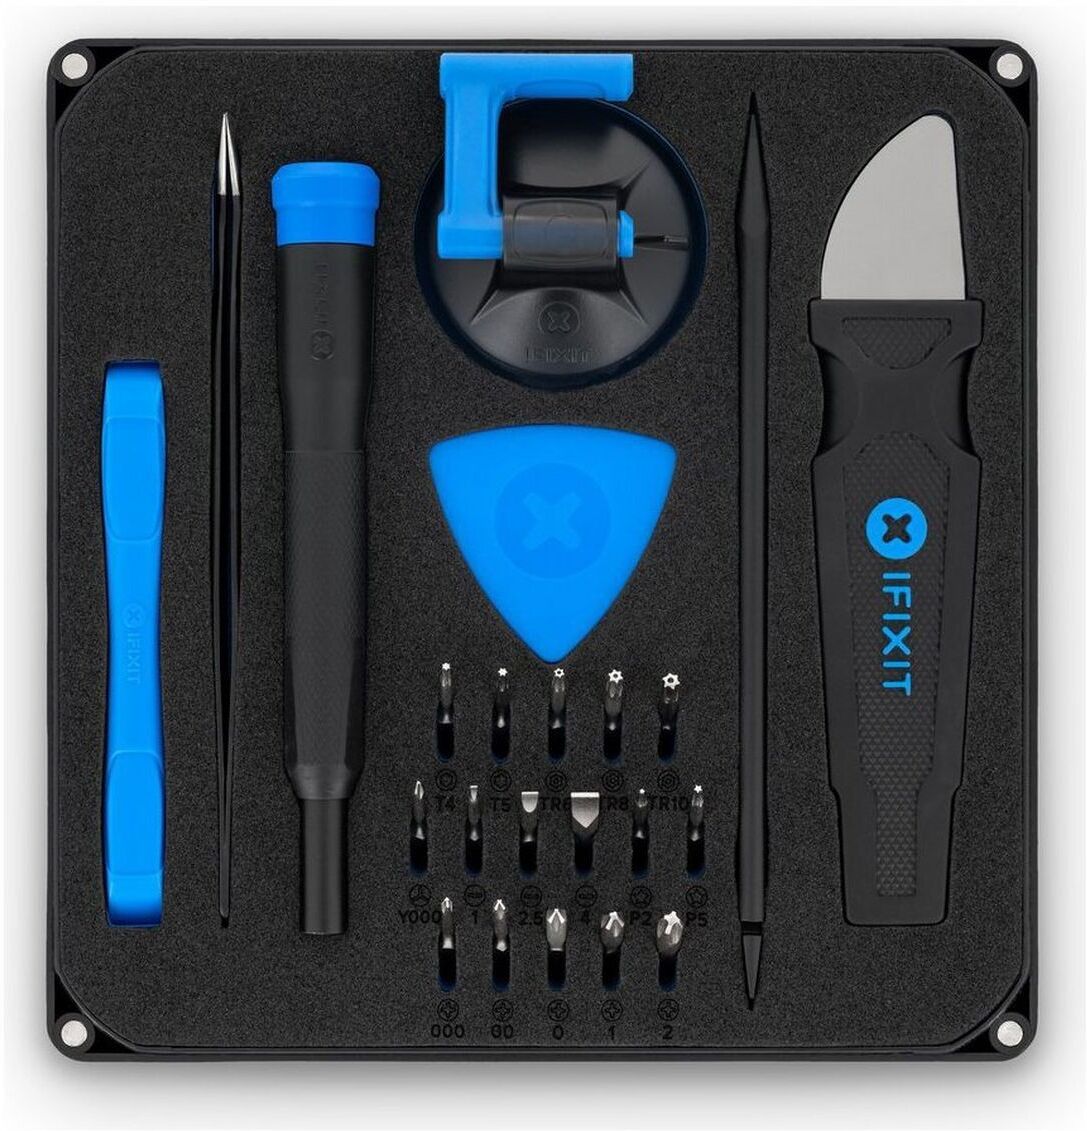
iFixit Essential Electronics ToolkitThe iFixit Essential Electronics Toolkit is a compact starter repair kit for phones, tablets, laptops, game consoles and other small electronics. It includes a precision bit driver with 16 precision bits plus the basic opening and prying tools needed for common repairs such as screen and battery replacements.40,99 £*Shipping: 0,00 £Secure redirect to the provider
-
Sesderma Reti Age 5 Liposomal Serum Anti-Aging Innovation 30mLA facial serum for wrinkles and signs of ageing. Reduces wrinkles and fine lines. Hydrates and strengthens barrier. Restores youthful radiance. 5-Retinoid System: smooths wrinkles, accelerates renewal, and boosts collagen. Biomimetic Peptides: fill expression lines by stimulating collagen synthesis.41,69 £*Shipping: 5,34 £Secure redirect to the provider
-
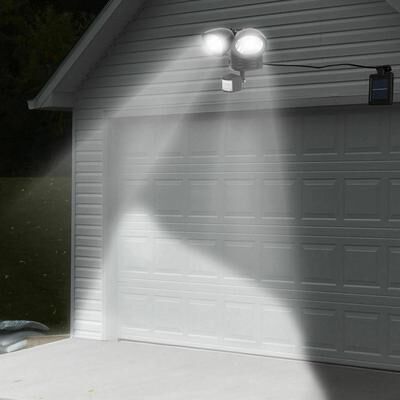
All Categories Goods LED Solar Security Light Dual Motion Sensor Outdoor Floodlight With LED Technology For Energy Efficient Illumination LED Solar Security Light Dual Motion Sensor Outdoor Floodlight With LED Technology For Energy Efficient IlluminationBrighten your outdoor space with the 1 pcs of 22 LED Solar Security Light, designed for maximum visibility and security. Powered by ecofriendly solar energy, this motion sensor floodlight activates when movement is detected, offering both...63,97 $*Shipping: 0,00 $Secure redirect to the provider


-
How do I block everything except Tor with iptables?
To block everything except Tor with iptables, you can create a rule to allow traffic only through the Tor network. First, allow traffic to the Tor network by adding a rule to allow outbound traffic on the Tor port (usually 9050 or 9150) using the command: ```bash sudo iptables -A OUTPUT -p tcp --dport 9050 -j ACCEPT ``` Then, block all other outbound traffic by adding a rule to drop all other outgoing connections: ```bash sudo iptables -A OUTPUT -j DROP ``` This will ensure that all outbound traffic is blocked except for the traffic going through the Tor network. **
-
Why is the port not being allowed in iptables?
The port may not be allowed in iptables because the corresponding rule to allow traffic on that port may not have been added. This could be due to an oversight or mistake in configuring the iptables rules. Additionally, the port may be blocked by a default deny rule in iptables, which prevents any traffic from passing through unless specifically allowed. It's also possible that the service or application listening on that port is not running or is misconfigured, which would prevent iptables from allowing traffic to that port. **
-
How can I use iptables on the Asus RT-AC66U?
To use iptables on the Asus RT-AC66U, you can access the router's web interface by entering its IP address in a web browser. Once logged in, navigate to the "Administration" tab and then select "System" and "Enable JFFS custom scripts and configs." This will allow you to create custom iptables rules in the router's firewall script. You can then add your desired iptables rules to the firewall script to control network traffic according to your preferences. Remember to save your changes and reboot the router for the new rules to take effect. **
-
How can I block the SSH port from outside using iptables?
To block the SSH port (port 22) from outside using iptables, you can use the following command: ``` sudo iptables -A INPUT -p tcp --dport 22 -j DROP ``` This command adds a rule to the INPUT chain of iptables to drop any incoming TCP traffic on port 22, effectively blocking SSH access from outside. Make sure to save the iptables rules so they persist after a reboot by using the `iptables-save` command. Keep in mind that blocking the SSH port may lock you out of your server if you are not careful, so it's important to have an alternative way to access the server in case of any issues. **

What does an electronics technician specializing in information and communication technology earn?
An electronics technician specializing in information and communication technology can earn an average salary of around $60,000 to $80,000 per year, depending on factors such as experience, location, and employer. With additional certifications or advanced degrees, they may be able to command higher salaries. Overall, this field offers competitive wages and opportunities for career growth as technology continues to advance. **
How much does an electronics technician for information and communication technology earn?
The salary of an electronics technician for information and communication technology can vary depending on factors such as experience, location, and employer. On average, in the United States, an electronics technician in this field can earn between $40,000 to $70,000 per year. However, with more experience and specialized skills, technicians can earn higher salaries, potentially exceeding $80,000 annually. It's important to research specific companies and regions to get a more accurate idea of salary expectations. **
Top-Angebote
Products related to Iptables:
-
Kami Mini Indoor 1080p Wi-Fi Security Camera by YI Technology (YYS.2919) - WhiteKeep an eye on your home with the Kami Mini indoor security camera by YI Technology. It records 1080p Full HD video through a 112° wide-angle f/2.0 lens, with infrared night vision for low light and two-way audio through the built-in microphone and speaker. Face, human and sound detection help cut down unnecessary alerts, and motion notifications are sent to the Kami/YI app in real time. Footage can be saved to a microSD card or to YI cloud storage, and the camera works with Amazon Alexa.34,49 £*Shipping: 0,00 £Secure redirect to the provider
-
iFixit Essential Electronics ToolkitThe iFixit Essential Electronics Toolkit is a compact starter repair kit for phones, tablets, laptops, game consoles and other small electronics. It includes a precision bit driver with 16 precision bits plus the basic opening and prying tools needed for common repairs such as screen and battery replacements.40,99 £*Shipping: 0,00 £Secure redirect to the provider
-
What is an alternative to iptables?
An alternative to iptables is nftables, which is a newer and more powerful packet filtering framework for Linux. Nftables provides a more user-friendly syntax and better performance compared to iptables. It also offers additional features such as stateful firewalling, easier rule management, and better integration with the Linux kernel. Overall, nftables is a modern replacement for iptables and is recommended for those looking for a more advanced and efficient packet filtering solution. **
-
Hello, I have a question regarding iptables.
Sure, I'd be happy to help. What specific question do you have about iptables? **
-
How do I block everything except Tor with iptables?
To block everything except Tor with iptables, you can create a rule to allow traffic only through the Tor network. First, allow traffic to the Tor network by adding a rule to allow outbound traffic on the Tor port (usually 9050 or 9150) using the command: ```bash sudo iptables -A OUTPUT -p tcp --dport 9050 -j ACCEPT ``` Then, block all other outbound traffic by adding a rule to drop all other outgoing connections: ```bash sudo iptables -A OUTPUT -j DROP ``` This will ensure that all outbound traffic is blocked except for the traffic going through the Tor network. **
-
Why is the port not being allowed in iptables?
The port may not be allowed in iptables because the corresponding rule to allow traffic on that port may not have been added. This could be due to an oversight or mistake in configuring the iptables rules. Additionally, the port may be blocked by a default deny rule in iptables, which prevents any traffic from passing through unless specifically allowed. It's also possible that the service or application listening on that port is not running or is misconfigured, which would prevent iptables from allowing traffic to that port. **
Similar search terms for Iptables
-
Sesderma Reti Age 5 Liposomal Serum Anti-Aging Innovation 30mLA facial serum for wrinkles and signs of ageing. Reduces wrinkles and fine lines. Hydrates and strengthens barrier. Restores youthful radiance. 5-Retinoid System: smooths wrinkles, accelerates renewal, and boosts collagen. Biomimetic Peptides: fill expression lines by stimulating collagen synthesis.41,69 £*Shipping: 5,34 £Secure redirect to the provider
-
All Categories Goods LED Solar Security Light Dual Motion Sensor Outdoor Floodlight With LED Technology For Energy Efficient Illumination LED Solar Security Light Dual Motion Sensor Outdoor Floodlight With LED Technology For Energy Efficient IlluminationBrighten your outdoor space with the 1 pcs of 22 LED Solar Security Light, designed for maximum visibility and security. Powered by ecofriendly solar energy, this motion sensor floodlight activates when movement is detected, offering both...63,97 $*Shipping: 0,00 $Secure redirect to the provider
-
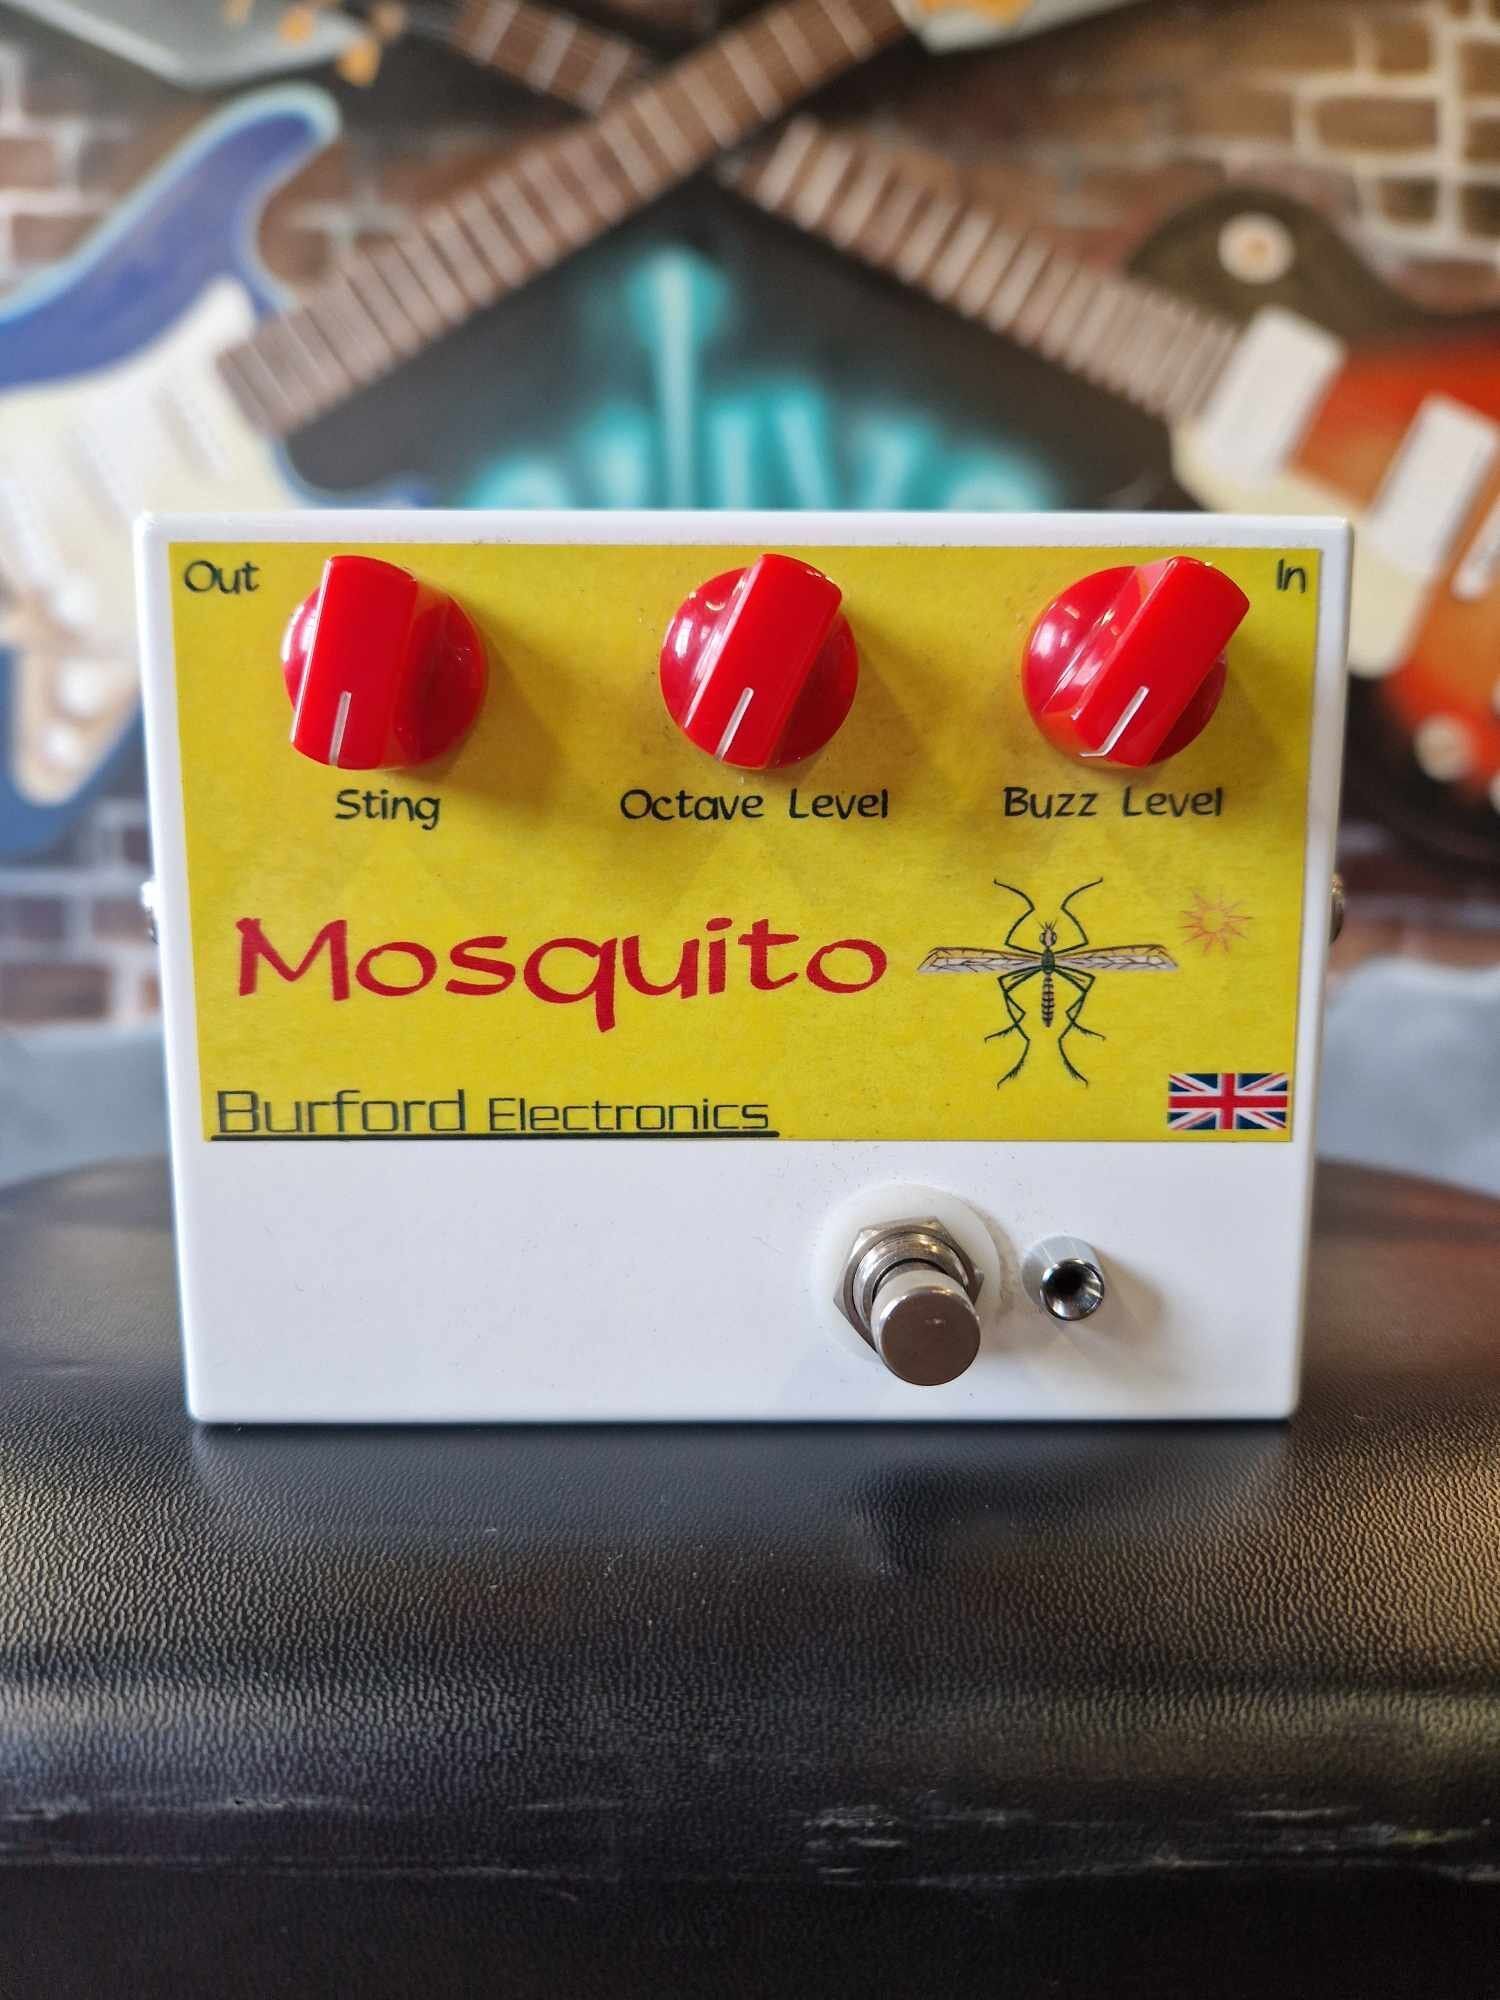
Burford Electronics Mosquito Fuzz Pedal Original - RefurbishedThis is a Burford Electronics Mosquito Fuzz Pedal. The Mosquito is a Fuzz/Octave pedal with a pretty unique sound, being closer to a fuzz more than a distortion this pedal delivers high octane fuzz sounds that will leave a sting. Here's what Burford Electronics say about the Mosquito Pedal: “A unique Octave up fuzz, which will give you pure fuzz on one twist of a knob & octave fuzz on one twist of another knob. So you can have your fuzz setting for a rich body & add octave fuzz to it or turn the fuzz down & just use the octave fuzz control for cutting lead. There is also a control called Sting, this is a tone filter that alters the voice of the octave from sharp to mellow. The octave is not over the top, on the lower register it is quite subtle, you can even play power chords and it holds together extremely well. Without that horrible modulation that is associated with some analogue octave up pedals, even some of the legendary expensive ones. Try soloing somewhere from the 8th fret upwards, it is very responsive and particularly so around 12th/15th fret and even higher. Neck and back pick ups give different sounds. Even playing positions will give different responses.”120,00 £*Shipping: 0,00 £Secure redirect to the provider
-
How can I use iptables on the Asus RT-AC66U?
To use iptables on the Asus RT-AC66U, you can access the router's web interface by entering its IP address in a web browser. Once logged in, navigate to the "Administration" tab and then select "System" and "Enable JFFS custom scripts and configs." This will allow you to create custom iptables rules in the router's firewall script. You can then add your desired iptables rules to the firewall script to control network traffic according to your preferences. Remember to save your changes and reboot the router for the new rules to take effect. **
-
How can I block the SSH port from outside using iptables?
To block the SSH port (port 22) from outside using iptables, you can use the following command: ``` sudo iptables -A INPUT -p tcp --dport 22 -j DROP ``` This command adds a rule to the INPUT chain of iptables to drop any incoming TCP traffic on port 22, effectively blocking SSH access from outside. Make sure to save the iptables rules so they persist after a reboot by using the `iptables-save` command. Keep in mind that blocking the SSH port may lock you out of your server if you are not careful, so it's important to have an alternative way to access the server in case of any issues. **
-
What does an electronics technician specializing in information and communication technology earn?
An electronics technician specializing in information and communication technology can earn an average salary of around $60,000 to $80,000 per year, depending on factors such as experience, location, and employer. With additional certifications or advanced degrees, they may be able to command higher salaries. Overall, this field offers competitive wages and opportunities for career growth as technology continues to advance. **
-
How much does an electronics technician for information and communication technology earn?
The salary of an electronics technician for information and communication technology can vary depending on factors such as experience, location, and employer. On average, in the United States, an electronics technician in this field can earn between $40,000 to $70,000 per year. However, with more experience and specialized skills, technicians can earn higher salaries, potentially exceeding $80,000 annually. It's important to research specific companies and regions to get a more accurate idea of salary expectations. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.